How Detection Governance Fixes ATT&CK Coverage Gaps
Why ATT&CK coverage breaks across SIEM, EDR, BAS and CTI — and how detection governance restores reliable mapping, effectiveness tracking, and detection health.
Read on secumap.co.ukDetection governance, MaGMa maturity, and the Detection System of Record (DSoR) — written for security teams who need to prove detection works, beyond a coverage count. Start with what is a Detection System of Record, or explore the latest articles below. Most posts connect threat priorities to declared, validated, and operational outcomes across detection coverage, detection effectiveness, and the health that keeps detections working in production.
Why ATT&CK coverage breaks across SIEM, EDR, BAS and CTI — and how detection governance restores reliable mapping, effectiveness tracking, and detection health.
Read on secumap.co.uk
Autonomous models surface gaps you already had: declared and validated are not operational. Why validation decay and production telemetry drift matter more than tool capability narratives.
Read on secumap.co.uk
Why static ATT&CK mapping and rule counts create false confidence, and how to measure coverage quality with governance and validation.
Read on secumap.co.uk
When validation fails, the rule is not always the problem. Why telemetry pipeline health and detection platform operations are the missing variables — and how teams misread infrastructure failure as bad logic.
Read on secumap.co.uk
How to move from rule throughput metrics to governed lifecycle outcomes across engineering, SOC, and leadership reporting.
Read on secumap.co.uk
How to use BAS as a governance input and connect simulation evidence to engineering remediation and production outcomes.
Read on secumap.co.ukMITRE ATT&CK is widely used to map detection coverage, but coverage is often mistaken for effectiveness. This article explores why detection maturity matters and where MaGMa fits.
Read on Medium
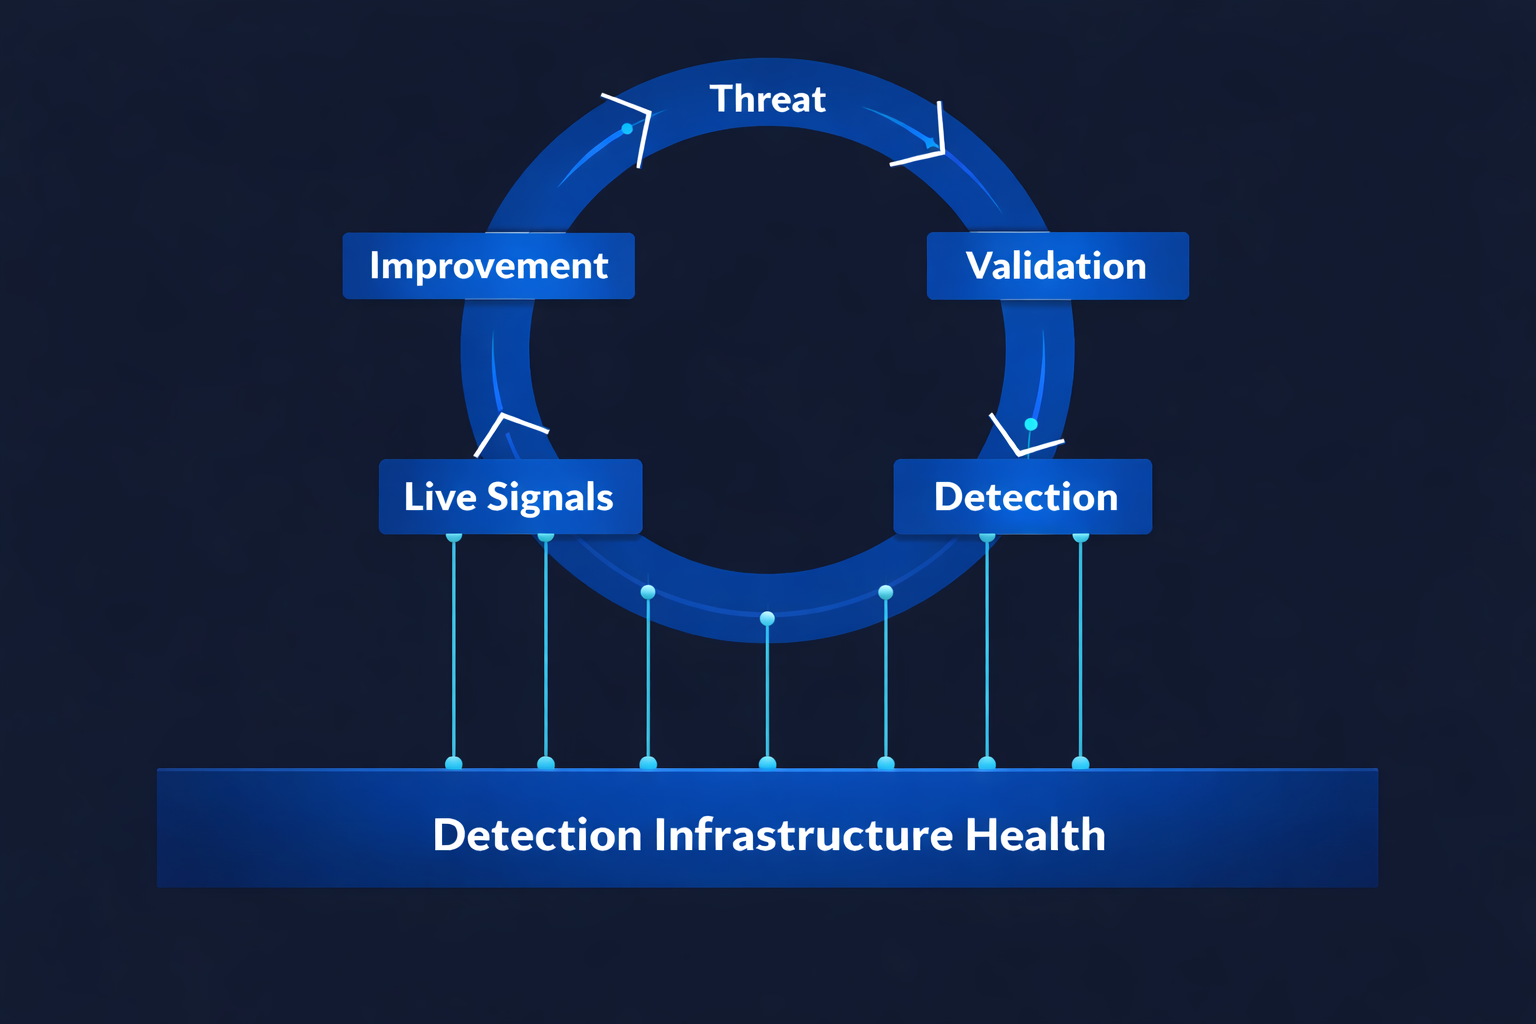
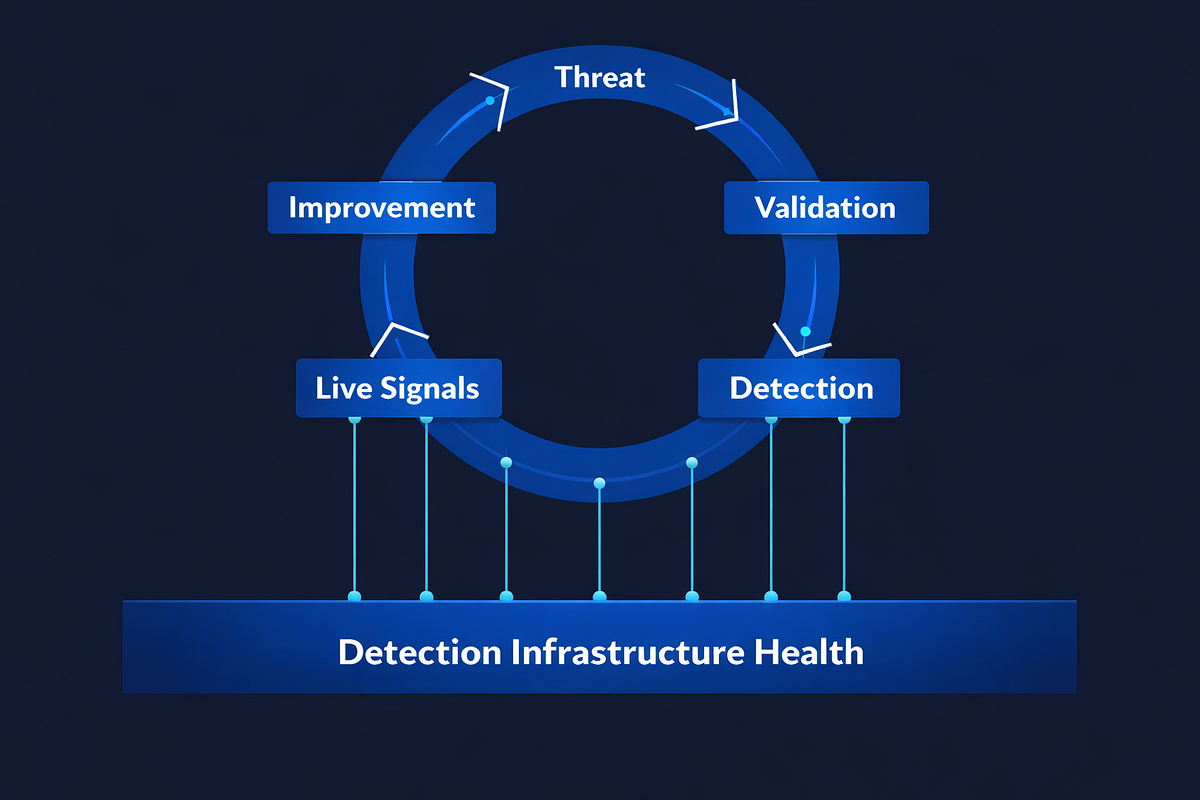
Why better security tooling will never solve what only an operating model can fix. Introducing Detection Infrastructure Health as the hidden variable in threat-informed defence.
Read on MediumSecuMap also syndicates selected posts on Medium. Use this index for the canonical on-site reading path, or follow Medium for the same author feed.
View all posts on Medium